
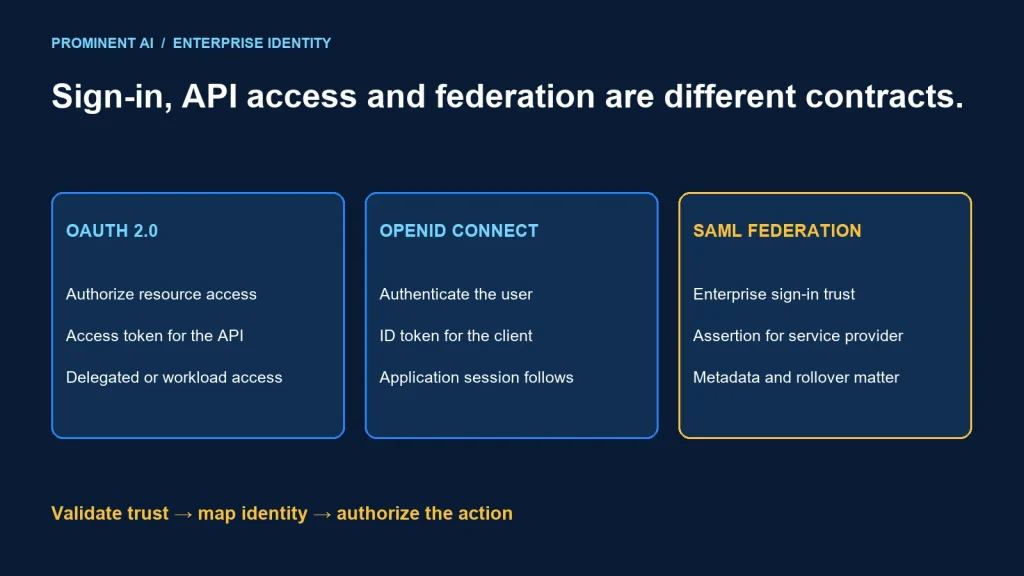
Use OAuth 2.0 for delegated or application access to protected resources, OpenID Connect for user authentication on top of OAuth, and SAML when a supported enterprise federation contract requires it. They are not three interchangeable token formats. A system can use SAML for a workforce application and OAuth access tokens for its APIs.
Key takeaways
- Authentication establishes identity; authorization decides permitted access.
- An ID token is for the client that requested sign-in, not a substitute for an API access token.
- Protocol selection depends on the application and identity provider’s supported, secure integration path.
- Tenant admission, local permissions, provisioning and session lifecycle remain application responsibilities.
OAuth vs OpenID Connect vs SAML
Start with the question being answered. Is a person signing in to an application? Is an application calling an API for a person? Is a background service accessing a resource without an interactive person? These are distinct trust relationships even if they share one identity platform.
The OpenID Connect Core specification defines an identity layer over OAuth 2.0 and an ID token carrying claims about authentication. The client validates that token for its own sign-in flow. It does not send it to a business API as an access credential.
Microsoft’s SAML SSO guidance describes an authentication request from a service provider and a response from the identity provider. SAML uses XML-based assertions and established federation configuration. Evaluate the exact supported profile, not just the presence of a SAML checkbox.
| Choice | Primary purpose here | Artifact and recipient | Typical scenario |
|---|---|---|---|
| OAuth 2.0 | Access authorization framework | Access token intended for a resource/API | Client invokes an approved API operation |
| OpenID Connect | User authentication over OAuth | ID token intended for the sign-in client | Modern application sign-in |
| SAML 2.0 federation | Enterprise federated authentication | SAML assertion/response for the service provider | Workforce application with a supported SAML integration |
Access tokens are not universally JWTs. Their format and validation contract belong to the issuer and intended resource. A client should not build application behavior by decoding an access token that it does not own.
SSO is a user experience supported by identity sessions and application integrations. It is not a guarantee that every application has the same session lifetime, logout behavior or permission model. Provisioning a local account is another separate lifecycle decision.
Token and trust-flow diagrams
Interactive application with OpenID Connect and an API
User → application → identity provider sign-in
Application receives authorization response
Client exchanges code using its supported secure flow
  ├─ ID token → client validates sign-in → local application session
  └─ access token → intended API validates → operation authorization
API still checks the user's permitted tenant, object and action.
This is a conceptual code-flow sketch, not a complete protocol implementation. Use maintained identity libraries and the provider’s current flow guidance. Browser, native and server-side clients differ in credential storage and token-handling responsibilities.
SAML workforce application
User → service provider → identity provider authentication
Identity provider → signed SAML response → approved consumer endpoint
Service provider validates response/assertion and correlation
Service provider maps identity → local session → local permissions
The browser transports messages in common SSO flows; it is not the authority that makes a claim trustworthy. The application relies on configured issuer trust, signature validation and protocol checks. Do not create a local login from a decoded assertion alone.
Background service calling an API
Approved workload identity → token issuer → access token for target API
Target API → validate token → authorize application permission → operation
No interactive user or ID token is required for this workload.
Prefer a supported workload identity mechanism where available, and document ownership of any certificate or secret. A service identity should receive only the resource permissions it needs. Do not give it a human administrator’s broad access merely to simplify integration.
An enterprise authentication decision matrix
| Situation | Candidate | Verify before choosing |
|---|---|---|
| New interactive web or native application | OIDC with supported secure flow | Client type, redirect handling, session and library support |
| Existing SaaS product supports SAML federation | SAML integration | Metadata, signatures, claim mapping and certificate rollover |
| Application calls a business API for a user | OAuth delegated access | Target audience, scopes, consent and user authorization |
| Scheduled integration has no user | OAuth application/workload access where supported | Application permissions, credential lifecycle and tenant admission |
| Legacy app cannot implement federation directly | Supported intermediary or modernization path | Trust boundaries, headers, session behavior and vendor support |
Do not add a translation layer simply because a protocol seems newer. A working supported SAML workforce application may be a sensible integration. Prioritize gaps such as weak account lifecycle, unsupported libraries or poor access control rather than changing formats without a business need.
A fictional enterprise portal might use OIDC for employee sign-in, OAuth access tokens for a document API and SAML for an older procurement product. That is not inherently inconsistent. Each relying application needs its own explicit trust and authorization contract.
Validation is different from reading claims
Decode only to inspect during controlled troubleshooting; validation is what establishes trust. APIs need the intended issuer and audience, valid cryptographic verification, appropriate lifetime checks and the resource’s authorization rules. Applications must reject tokens intended for a different resource even when the signature is valid.
For OIDC, follow the library and provider requirements for request correlation, state and nonce handling. Maintain an explicit redirect-URI configuration. The OAuth 2.0 Security Best Current Practice, RFC 9700 updates security guidance, including protection of authorization-code flows and PKCE. Avoid implementing older flows from an outdated tutorial without reviewing that guidance.
For SAML, use a maintained library that enforces the supported profile, signature expectations, audience, destination, validity and response correlation. Never bolt together XML parsing and manual signature checks as a shortcut. Confirm replay protection and metadata update behavior with the implementation.
Keep tenant admission separate from successful authentication. In a multi-tenant product, a valid identity from an external organization does not automatically make that organization a customer. Map validated identities to approved local tenants and memberships before granting access to tenant data.
Use stable provider identifiers and a documented mapping strategy. Email addresses can change and may not be unique across all identity arrangements. Account linking needs an intentional verification process; a matching display name is not evidence that two accounts belong to one person.
Permissions need a clear owner. External groups, application roles and local entitlements can support different policies. Define what happens when a person changes department, loses a role or leaves the organization, including any delay before active sessions reflect the change.
Sessions, provisioning and troubleshooting
Plan identity operations before the happy-path demo. Someone must own certificate rollover, credential expiry, metadata trust, redirect changes and incident response. Test those changes before an expiring certificate causes an outage.
Login, local account creation and access removal should be independently observable. SSO does not automatically provide complete joiner/mover/leaver automation. Determine whether the product supports provisioning and deprovisioning, and verify local-session behavior after access removal.
| Symptom | Investigate | Controlled correction |
|---|---|---|
| Sign-in succeeds but API rejects | Token type, audience and permission | Request the correct resource token and authorize its action |
| Redirect or consumer endpoint mismatch | Registered environment URLs | Correct the approved URI configuration |
| Outage after certificate change | Signing trust and rollover process | Update trusted metadata through the supported path |
| Wrong tenant data becomes visible | Local tenant mapping and object authorization | Reject unapproved mappings and enforce data boundaries |
| Removed user retains access | Provisioning and application sessions | Apply documented access-removal and session controls |
Log correlation identifiers and failure categories, not raw tokens, assertions or secrets. Give support teams enough context to distinguish failed authentication from denied authorization without exposing credentials through screenshots and ticket attachments.
Test logout and session expiry independently for each application. Signing out of one local session may not end every identity-provider or application session. Explain the actual user experience rather than promising universal instant logout.
A practical integration and migration plan
- Inventory applications, client types, identity providers and API calls.
- Separate sign-in, resource access and provisioning requirements.
- Confirm supported protocols and maintained libraries.
- Define issuer trust, environment URLs and identifier mapping.
- Model local roles, tenant admission and object-level access.
- Test wrong audience, expired credentials, replay and invalid correlation.
- Exercise onboarding, offboarding, rollover and recovery.
- Roll out to a bounded group with support and rollback ownership.
For a migration, preserve a verified mapping between old and new identities before enabling users broadly. Avoid silently merging accounts based on a mutable profile field. Reconcile entitlements and audit records so users retain only intended access.
This article provides an architecture decision framework, not a complete security implementation. Review the exact provider, application library and threat model. See the multi-tenant authentication guide and integration architecture comparison for related design boundaries.
Common questions
When should an application use OAuth, OIDC or SAML?
Use OAuth for resource access, OIDC for user sign-in over OAuth, and SAML for an appropriate supported federation integration. Several may coexist.
Can an ID token be used to call an API?
Use the API’s intended access token. An ID token establishes sign-in for its client and is not a substitute for the API’s access contract.
Is SAML obsolete for enterprise SSO?
A supported SAML integration can remain appropriate. Evaluate application support, lifecycle controls and security rather than age alone.
Does SSO automatically remove accounts when staff leave?
No. Provisioning, deprovisioning and local-session behavior need explicit configuration and verification.
Does a valid token grant access to every tenant?
No. Validate the token, then enforce approved tenant membership, roles and access to the requested object and action.
Choose the right trust contract for each application
Bring your identity providers, applications and resource-access requirements. Request an API integration architecture review to define federation, API access and lifecycle responsibilities.