
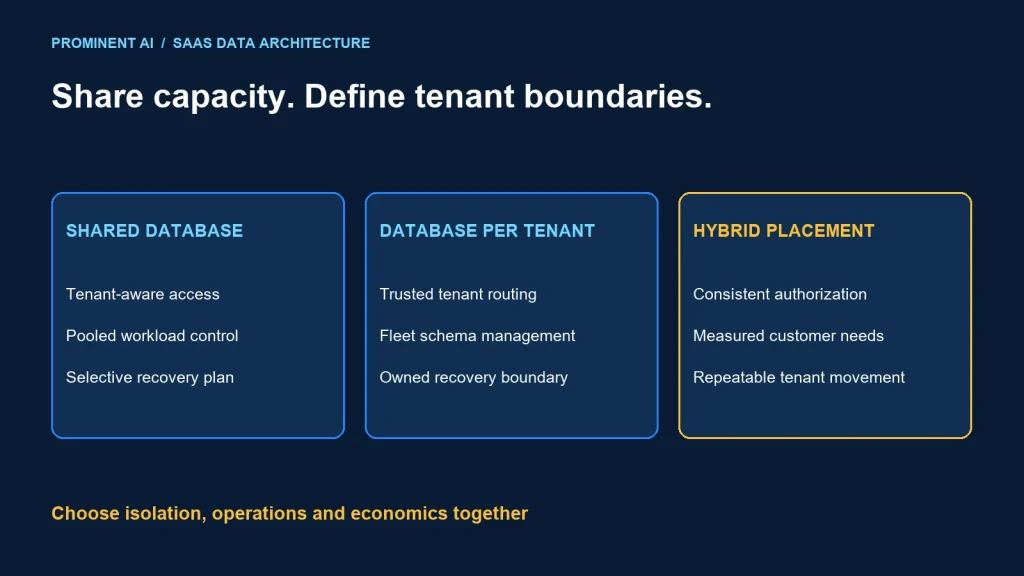
Database per tenant gives each customer a separate data-management boundary; a shared database pools tenant records behind enforced tenant-aware access. The best multi tenant SaaS architecture depends on isolation, recovery, scale and operating economics. Many B2B products benefit from a hybrid design, but only when tenant placement and lifecycle operations are automated and tested.
Key takeaways
- Application tenancy and database tenancy are separate decisions.
- A separate database does not automatically provide separate compute, credentials or complete security isolation.
- Shared data requires tenant-aware authorization across APIs, jobs, caches and reporting.
- Compare onboarding, schema upgrades, restore and offboarding alongside monthly database charges.
Two data-tenancy architecture diagrams
Microsoft’s multitenant data guidance evaluates sharing and isolation alongside tenant workload, lifecycle and operational requirements. Azure SQL’s tenancy pattern guide describes shared, database-per-tenant and hybrid options. Use the patterns to shortlist a design, not to assume one model fits every customer.
Database per tenant
Authenticated request → authorized tenant context
→ trusted tenant catalog → connection selection
├─ Tenant A → Database A
├─ Tenant B → Database B
└─ Tenant C → Database C

Fleet operations: provision, migrate, monitor, restore and retire
Compute or server resources may still be shared.
The catalog is a security-sensitive routing component. The application must derive the tenant from an authenticated and authorized context, then resolve an approved location. It must not accept an arbitrary database connection or tenant identifier as proof of entitlement.
Shared database
Authenticated request → authorized tenant context
→ tenant-scoped application operation → shared database
├─ Records for Tenant A
├─ Records for Tenant B
└─ Records for Tenant C

Tenant-aware keys, constraints, queries and permissions
Optional database RLS where supported and correctly configured
Pooling can simplify some fleet management, but it concentrates data and shared resource behavior. Treat missing tenant context as an error. Administrative and analytics paths need explicit cross-tenant authority rather than silently bypassing the ordinary rules.
Compare workload behavior, not just database count
| Area | Database per tenant | Shared database |
|---|---|---|
| Data boundary | Separate database with correctly scoped access | Tenant separation within shared structures |
| Performance | Can allocate or pool resources by tenant design | Requires management of pooled workload contention |
| Schema upgrades | Fleet rollout and version tracking | One schema change can affect many tenants |
| Tenant recovery | Potentially more granular database recovery | Tenant-selective recovery requires careful extraction and reconciliation |
| Analytics | Cross-database aggregation needs an owned path | Aggregation can be simpler but must remain authorized |
| Economics | Resource and fleet-management overhead | Pooled capacity plus isolation and tenant-operation engineering |
For a product with many small customers, pooling can be attractive if access boundaries and shared performance are well managed. A large tenant with distinct recovery or placement needs can justify dedicated data resources. These are decision hypotheses to validate, not automatic rules based on tenant count.
Define the unit of isolation. A database can be separate while application processes, connection credentials, backups or server capacity remain shared. Write down the boundary promised commercially and the controls that actually enforce it.
Tenant isolation and row-level security
Enforce tenant authorization before selecting data. Validate membership and role permissions server-side. A browser route, header or query parameter can identify a requested tenant, but it cannot establish the caller’s right to use it.
For shared tables, carry tenant identity through keys, relationships and writes. Review whether uniqueness constraints and foreign keys must include the tenant dimension. A query filter cannot repair a relationship that permits one tenant’s record to reference another’s data.
Row-level security can provide an additional database enforcement layer where the chosen engine supports it. Validate session context, elevated roles and policy behavior, especially with connection pooling. Do not assume a single application filter or RLS policy covers raw SQL, background jobs, exports and support tooling automatically.
Scope caches, object storage paths, search indexes and messages as well as relational records. A correct SQL predicate does not prevent a cache key collision from returning another tenant’s response.
For database-per-tenant, restrict credentials and routing. A broadly privileged application identity coupled with an incorrect catalog mapping can still cross the intended boundary. Test both access denial and wrong-destination prevention.
Isolation tests to include
- A user from tenant A cannot access tenant B by changing an identifier.
- Missing or malformed tenant context fails closed.
- Background work retains its authorized tenant scope.
- Connection reuse does not retain the previous tenant’s context.
- Exports, search and support operations obey their access contract.
- Administrative cross-tenant access is explicit and auditable.
Migrations, recovery and tenant lifecycle
Database-per-tenant requires a fleet schema registry, controlled migration waves and clear handling of partial failure. Record which application versions can serve each schema version. A failed migration for one customer should not be hidden behind an overall deployment success badge.
For a shared database, test migration impact across tenant workload shapes. Large tables, concurrent writes and long transactions can change the release risk. Use compatible staged changes where old and new application versions coexist.
Restore is a business workflow, not only a backup feature. In a shared store, restoring the entire database can roll other tenants back unintentionally. A selective process may need a temporary restore, tenant-specific extraction, integrity checks and reconciliation with newer external actions.
A dedicated database can make the recovery boundary clearer, but related files, search indexes and messages may live elsewhere. Prove the complete tenant recovery objective, including dependencies and validation by the responsible owner.
Automate onboarding and offboarding. Provision or place data, register the catalog entry, configure access, verify readiness and record the result. Retirement should address retention, exports, credentials and related resources under the approved lifecycle policy.
For a tenant move, establish a source of authority, copy and reconcile data, manage writes during cutover, update routing and define a rollback boundary. Avoid uncontrolled simultaneous writes to both locations.
Billing, metering and SaaS pricing
Separate internal cost allocation from customer pricing. Database consumption is only part of the product cost: application compute, storage, network, support, observability, recovery and engineering effort also matter.
Capture tenant-attributable usage where appropriate and protect the metering path from duplication or loss. A shared database bill alone cannot tell finance how much each tenant consumed. A dedicated database bill may still exclude the tenant’s share of common services.
| Cost area | Question for the model |
|---|---|
| Base capacity | What remains provisioned when tenants are idle? |
| Variable consumption | Which operations, storage and transfer grow with use? |
| Fleet operations | How much automation and support does the model require? |
| Recovery | What does tenant-specific restoration cost to execute and test? |
| Premium isolation | Which resources and responsibilities are genuinely dedicated? |
| Tenant movement | What does migration between tiers require? |
For an illustrative allocation method, distribute a common monthly platform cost by an agreed combination of base tenancy and measured consumption. Record that this is a management model, not exact physical attribution. Test whether it distorts decisions for large or unusually active tenants.
Do not advertise dedicated isolation simply because a commercial plan has a higher price. Make the technical boundary, support service and recovery commitment explicit. Verify current service pricing and commercial terms before promising margins or savings.
A selection matrix for B2B SaaS
| Requirement | Candidate direction | Evidence |
|---|---|---|
| Many small tenants with similar requirements | Shared or sharded pools | Isolation tests and representative contention testing |
| Distinct tenant restore or placement needs | Dedicated database or deployment boundary | Full recovery and routing rehearsal |
| Large variation in workload | Hybrid placement with clear tiers | Metering, capacity thresholds and tenant movement |
| Limited fleet automation | Reduce operational variation before scaling | Repeatable onboarding and schema upgrades |
| Unclear tenant authorization | Resolve identity and access contract first | Denied cross-tenant tests across every access path |
A hybrid design needs one trusted placement model and consistent application authorization across pools. It is not a collection of manual customer exceptions. Keep schema policy, monitoring and migrations manageable as the estate grows.
Evaluate module boundaries through the .NET modular monolith guide and identity boundaries through the Azure access-path review.
Common questions
Which database tenancy model is best for B2B SaaS?
Choose from isolation, recovery, workload and operating requirements. Shared, dedicated and hybrid models can all be appropriate when their boundaries are enforced and tested.
Does database per tenant guarantee complete isolation?
No. Application identity, routing, shared compute and related resources can still cross boundaries. Define and validate the full promised isolation scope.
Is row-level security enough for shared tenancy?
It can strengthen database enforcement, but application authorization, session handling and every non-database access path still need controls and tests.
Can we restore one tenant from a shared database?
Design and rehearse a tenant-selective process. It may require a separate restore and extraction followed by integrity checks and reconciliation.
Can tenants move between shared and dedicated databases?
Yes, with an owned copy, reconciliation, cutover and routing workflow. The operation should be tested and repeatable rather than a manual exception.
Design tenancy around customer and operating commitments
Bring tenant sizes, isolation requirements and recovery expectations. Discuss your .NET modernization roadmap to compare SaaS data boundaries and a sustainable tenant lifecycle.